
Most small business owners assume their company is too small to attract active hackers. In reality, cybercrime relies on automated tools scanning for open vulnerabilities rather than specific brand names. Leaving your network unsecured guarantees your systems will eventually be discovered.
An email arrives from your CEO requesting an urgent, off-schedule wire transfer to secure a vendor deal. Standard operational caution gives way to speed, and cash is redirected to an unauthorized account. This is the result of a form of cyberattack known as business email compromise. Let’s discuss how to stop it.
Cybersecurity Awareness Month serves as a vital reminder that technical infrastructure relies heavily on human habits. A single compromised credential can expose your entire network to unauthorized access and operational downtime. Protecting company data is a shared organizational responsibility.
Many organizations continue running legacy software versions long past their official manufacturer support dates because the applications still execute basic daily tasks. That said, operating unpatched systems introduces severe security vulnerabilities that automated malware scans actively target. Failing to modernize your business’ software leaves your corporate data exposed to unauthorized access and system-wide failure. Let’s talk about how to shore up these vulnerabilities.
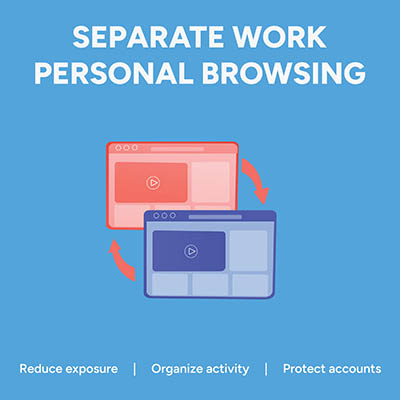
Picture this: an employee is logged into their personal Google or Microsoft account to check a personal email. In the very next tab, they open your company’s cloud dashboard to edit a sensitive spreadsheet. It feels completely harmless, but in reality, that single overlapping browser session is a quiet source of data leaks, compliance headaches, and constant calls to your IT help desk. That’s because if personal identities and corporate cloud accounts mingle in the same browser instance, the browser gets confused. It attempts to sync saved passwords, autofill data, browsing history, and extension permissions across both environments. The fix is simple… enforce dedicated browser profiles for your entire team.
Managing hundreds of business accounts with complex, frequently changed passwords no longer protects your organization. In fact, forcing arbitrary symbol substitutions and constant resets creates predictable patterns that hackers easily exploit. Modern security relies on practical, long-term rules that safeguard data without slowing down daily work.
When cybercriminals try to break into a business, they rarely bother picking digital locks. Instead, they send a convincing email straight to someone on your staff. Treating your team like a security liability creates fear and keeps people from reporting suspicious activity.
When your team is trying to get things done, they will usually take the path of least resistance. Sometimes, that means bringing outside tools into your daily workflow without asking permission first.
When a small business starts out, file sharing usually happens organically through email attachments, personal cloud drives, and quick chat links. While that gets work done in the beginning, scaling a business on unmanaged file habits creates serious operational snarls and major security vulnerabilities down the line.
Modern cybercriminals have modified their attack methodologies. Rather than immediately encrypting production servers, sophisticated network intruders quietly target secondary file archives first to prevent organizations from performing independent data restoration. If your enterprise data protection configuration permits the modification or erasure of backup logs, a security incident can result in the permanent destruction of your operational records and force costly operational downtime.